
NIGERIA’S MULTIBILLION-NAIRA BANK FRAUD CRISIS: HOW CYBERCRIMINALS AND INSIDERS ARE TARGETING CUSTOMERS
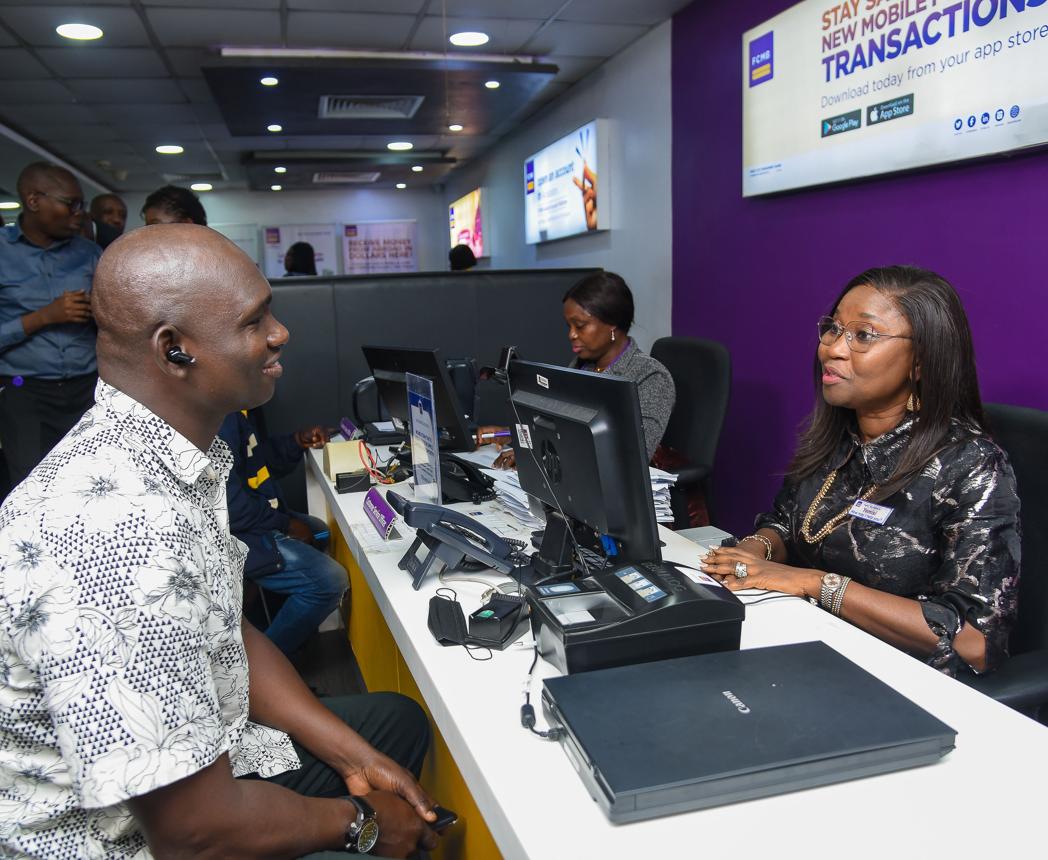
A 73-year-old retired University of Lagos worker reportedly lost approximately ₦3 million after experiencing problems with her bank's mobile application and later discovering unauthorised withdrawals. Her case has renewed concerns about cybercrime and possible insider involvement in Nigeria's banking sector. CBN and NIBSS figures show that fraud losses reached ₦134.48 billion cumulatively between 2020 and 2025, while major investigations involving SunTrust, Wema Bank, First Bank, Globus Bank and Hope Payment Service Bank illustrate the scale and complexity of attacks against financial institutions.
LAGOS, November 7, 2026 An elderly Lagos woman who lost approximately ₦3 million in what appears to have been an account-compromise incident has become the latest example of the growing security concerns surrounding Nigeria’s banking system, where cybercriminals are exploiting weaknesses in digital platforms, manipulating customers and, in some investigated cases, allegedly receiving assistance from employees with access to financial institutions’ internal systems.
The 73-year-old woman, identified by the pseudonym Agnes Uwaila, reportedly lost the money within hours after beginning to receive debit notifications on her bank account. According to an investigation published by Saturday PUNCH, the retired University of Lagos employee had visited her bank weeks earlier after experiencing difficulties with its mobile banking application. She reportedly approached the customer service section for assistance, but subsequently discovered that approximately ₦3 million had disappeared from her account.
A friend familiar with the incident told the newspaper that the money represented the woman's entire life savings, together with financial support sent by her daughters for her upkeep. The woman, who had retired after more than four decades working as a non-academic staff member at the university, depended on her pension and family assistance. The source said she collapsed after discovering the withdrawals and was taken to a hospital for medical attention.
The circumstances surrounding the alleged theft have raised questions about the security of customers' personal banking information and the procedures followed when bank employees assist customers experiencing difficulties with digital services. According to the friend, Uwaila said the customer service representative who attended to her had requested her personal identification number while attempting to resolve the application problem. The family has not established whether that interaction was directly connected to the subsequent withdrawals, whether her credentials were compromised through another method or whether the bank's systems were accessed without authorization.
The bank involved was not publicly identified in the report, and no conclusion has been established about the responsibility of any employee or the institution. Nevertheless, the account has renewed concerns about the risks customers face when they disclose sensitive information during routine banking interactions, particularly when they rely on employees to help resolve technical problems they may not fully understand.
Uwaila's experience was not the only account of suspicious withdrawals described in the investigation. A neighbour, identified only as Shola, said she had encountered a similar problem after visiting another bank to complain that its mobile application was not working. She reportedly began noticing withdrawals from her account several days after the visit, with the money taken in smaller amounts. She said the police became involved and that most of her money was eventually recovered.
The two accounts do not establish that the same individuals or methods were involved, nor do they prove that bank employees were responsible. They do, however, illustrate why customers are increasingly concerned about what happens to their personal and financial information when they seek assistance from institutions that hold their savings. In a banking environment where mobile applications, internet transfers and electronic payments have become routine, the security of customer credentials is as important as the protection of the financial infrastructure processing the transactions.
Nigeria's fraud figures show that the problem extends well beyond individual cases. Data contained in the Central Bank of Nigeria's Payments System Vision 2028 document indicate that banks and customers suffered cumulative fraud losses of approximately ₦134.48 billion between 2020 and 2025. The same document put the value of attempted fraud across the financial system during the period at approximately ₦187.79 billion, illustrating the scale of criminal activity directed at the country's increasingly digital financial sector.
Separate figures reported by the Nigeria Inter-Bank Settlement System show that digital payment fraud losses declined to ₦25.85 billion in 2025, from ₦52.26 billion in 2024, representing a reduction of approximately 51 per cent. The number of recorded fraud incidents also fell from 123,918 in 2021 to 67,518 in 2025. While the decline suggests that industry interventions and stronger controls may be having an effect, the remaining financial losses demonstrate that electronic fraud continues to impose a substantial cost on banks, payment providers and their customers.
The 2024 figures were particularly affected by a single major incident valued at approximately ₦31.1 billion, according to NIBSS. That event accounted for a significant share of the year's total losses and illustrates how a relatively small number of large-scale attacks can dramatically affect the industry's financial exposure. The reduction recorded in 2025 is therefore encouraging, but it does not mean that the underlying vulnerabilities have disappeared or that ordinary customers are no longer at risk.
Lagos accounted for approximately 63.43 per cent of fraud activity recorded in the NIBSS figures presented for 2025, reflecting the concentration of financial institutions, commercial transactions and digital payment activity in the state. Abuja followed with 3.12 per cent, while Ogun, Rivers and Delta states also featured in the distribution. The figures indicate the scale of exposure in the country's largest commercial centre, although the concentration of reported incidents should also be understood in the context of Lagos's much higher volume of financial transactions.
The methods used by criminals vary, but cybersecurity specialists identify phishing, malware, social engineering, account takeover, SIM-swap fraud and the misuse of employee credentials among the principal threats facing financial institutions and their customers. In many cases, criminals do not need to defeat an entire bank's security infrastructure. They may instead target a vulnerable customer, an employee with privileged access, an outdated application or an external service provider connected to the institution's systems.
Phishing operations typically involve fraudulent messages, emails, websites or telephone calls designed to persuade customers to disclose passwords, personal identification numbers, one-time passwords or other sensitive information. Criminals frequently impersonate banks or government institutions, using official-looking language and urgent warnings to create the impression that an account will be blocked or a transaction will fail unless the customer acts immediately. Once access has been obtained, the information can be used to take over an account, register another device or initiate unauthorised transactions.
Malware presents a different but equally serious threat. A malicious programme installed on a computer or mobile device can collect login credentials, record keystrokes, monitor activity or provide an attacker with remote access. Cybercriminals may distribute such software through deceptive links, compromised downloads, fake applications or malicious attachments. Employees can also become targets when attackers send fraudulent recruitment invitations, interview documents or software tools designed to compromise workplace computers.
A technology employee at a commercial bank told Saturday PUNCH that malware could be used to harvest information from devices and interfere with banking operations. The source also identified the possibility of insider compromise, either through deliberate collaboration between employees and external criminals or through staff members inadvertently opening malicious files that give attackers access to internal systems. Weak authentication, outdated software and poorly secured applications can make such intrusions easier.
The involvement of insiders is particularly concerning because bank employees may already possess legitimate access to systems that ordinary criminals cannot easily reach. An employee with excessive privileges, shared login credentials or inadequate supervision could potentially help an external attacker bypass controls, obtain customer information or manipulate transactions. In some cases, the employee may deliberately facilitate the operation; in others, criminals may steal or misuse the employee's credentials without the person's knowledge.
The Economic and Financial Crimes Commission has previously raised concerns about alleged collaboration between bank employees and external hackers. EFCC Chairman Olanipekun Olukoyede said investigators had uncovered coordinated cyberattacks involving six financial institutions in which employees allegedly assisted criminals by connecting devices to banking systems and enabling individuals outside Nigeria to control those systems remotely. He also said the agency had recovered billions of naira linked to some of the investigations.
The allegations demonstrate why insider threats cannot be treated simply as a matter of employee misconduct. They also raise questions about how banks control access to critical infrastructure, monitor staff activity and identify unusual transactions before money is transferred beyond the reach of investigators. Where an employee can use legitimate credentials to facilitate unauthorised access, conventional security measures focused primarily on external hackers may not be sufficient.
Several major investigations and prosecutions have exposed the financial consequences of weaknesses within banking institutions. In one case, SunTrust Bank Plc was targeted in cyberattacks over a period of approximately three years, with suspects accused of diverting more than ₦800 million through unauthorised access to the bank's systems. A suspect identified as Ugochukwu Eze, also known as Amazon, was arraigned before the Federal High Court in Lagos in August 2026. The investigation and subsequent court proceedings placed renewed attention on the ability of criminal networks to target financial institutions repeatedly.
Wema Bank also faced a major alleged breach in January 2025, when criminals were accused of manipulating internal computer data, authorisation procedures and transfer systems to divert approximately ₦8.5 billion. The EFCC subsequently arraigned three bank employees and four external individuals over the alleged scheme. In November 2025, a Lagos Special Offences Court convicted and sentenced one of the bank's employees, Ihechukwu Asiegbu, to three years in prison for unauthorised access to the bank's computer system to facilitate the theft. The proceedings provided a concrete example of how insider access can become part of a wider financial crime operation.
First Bank was also involved in a separate investigation after the institution initiated legal action in 2024 to recover approximately ₦40 billion allegedly diverted by an employee attached to its head office team in Iganmu, Lagos. The funds were reportedly transferred into 98 beneficiary accounts, including an account belonging to the employee's wife. The bank reported the matter to the police and obtained court orders to restrict accounts suspected of receiving the money. The allegations highlighted the difficulties financial institutions face when investigating transactions that may have been processed through internal systems using apparently legitimate credentials.
In another case, the EFCC prosecuted a former Globus Bank information technology employee accused of participating in the theft of approximately ₦3.5 billion from customer accounts. Investigators alleged that the defendants used shared employee login credentials to gain access to the bank's systems and transfer funds. The commission said approximately ₦1.2 billion had been recovered, while the accused ICT employee denied the allegations. The case illustrates the importance of restricting access to sensitive systems and ensuring that credentials assigned to individual employees cannot be casually shared or used without adequate monitoring.
The Hope Payment Service Bank incident in July 2024 further demonstrated the potential scale of cyber-related losses. Investigations and court proceedings placed the amount involved at figures ranging from approximately ₦6.5 billion to nearly ₦10 billion, with some prosecution figures citing losses of up to ₦9.68 billion. In October 2024, the Federal High Court in Abuja ordered the freezing of 818 accounts across commercial banks and digital financial institutions following an application by the Inspector-General of Police seeking to intercept and recover funds allegedly diverted from the institution.
These cases are not evidence that every bank employee or every digital banking platform is compromised. They do, however, demonstrate that the threat is not limited to customers being deceived into sharing their passwords. Criminals can also exploit weaknesses in institutional controls, compromise employee devices, abuse legitimate access and move money through networks of beneficiary accounts before the transactions are detected.
Cybersecurity expert David Odes told Saturday PUNCH that attackers often require only one vulnerable entry point to gain access to a much larger organisation. That weakness may involve an employee who has been targeted because of their level of access, unpatched software, poorly secured applications or an external company connected to the bank's infrastructure. He explained that banking applications rely on systems known as Application Programming Interfaces, which allow mobile and web platforms to communicate with backend services. If those interfaces do not properly authenticate users, verify permissions or process transactions securely, criminals may be able to exploit them.
The risk can extend beyond systems directly owned and managed by banks. Payment processors, technology vendors, outsourced service providers and other third-party organisations may have connections to financial infrastructure. A weakness in one of those organisations can create a route into another institution, making it necessary for banks to assess the security of their entire network of partners and service providers rather than concentrating only on their own computers and applications.
Odes also warned that sophisticated attackers may spend days or weeks inside a compromised network before attempting to steal money or information. During that period, they can examine internal systems, identify valuable data, obtain higher access privileges and locate the infrastructure used to authorise transactions. If unusual activity is not detected quickly, an initial compromise can develop into a much larger incident. Monitoring employee access, network traffic, application requests and transaction patterns can therefore be essential to identifying an attack before substantial losses occur.
The expert argued that banks should restrict access to critical systems according to employees' actual responsibilities, rather than allowing broad access simply because a person works within the organisation. He also identified regular penetration testing, independent security audits, network separation, continuous monitoring and properly staffed security operations teams as important elements of an effective defence. Such measures are designed to prevent an attacker who compromises one account or device from gaining control over an institution's wider infrastructure.
The human element remains another major vulnerability. Ethical hacker Khelly told the newspaper that curiosity, inadequate security awareness and poor employee practices can expose organisations to serious attacks. An employee who connects an unknown flash drive to a workplace computer, opens an infected attachment or ignores security procedures may unintentionally provide criminals with an opportunity to enter the network. Deliberate insider involvement creates an additional challenge, particularly where staff members have access to sensitive information or feel that internal controls are unlikely to detect their activities.
The Central Bank of Nigeria has increasingly emphasised the importance of stronger safeguards as the country's financial system expands its use of digital payment services. Its Payments System Vision 2028, officially presented in June 2026, identifies security, trust, inclusion, innovation, interoperability and collaboration as central principles for the future of the payments ecosystem. The framework places greater emphasis on regulatory supervision, consumer protection and the development of payment infrastructure capable of supporting a growing digital economy without exposing customers to unacceptable risks.
The regulator has also warned about fraudulent communications designed to impersonate the Central Bank. In an advisory, the CBN cautioned members of the public against clicking suspicious links or sharing personal information through websites and messages claiming to represent the institution. It said fake communications had been circulated using misleading claims about its leadership, licensing activities and policy decisions, with the apparent objective of obtaining personal information from unsuspecting recipients.
Nigeria's data protection framework also places obligations on organisations that experience certain forms of personal data breach. Section 40 of the Nigeria Data Protection Act 2023 requires a data controller to notify the Nigeria Data Protection Commission within 72 hours after becoming aware of a breach likely to create a risk to individuals' rights and freedoms. Where a breach presents a high risk to affected individuals, the law also requires communication with those individuals without undue delay. These obligations are important because compromised personal information can be used for identity theft, account takeover and other forms of financial crime long after an initial security incident has occurred.
However, the responsibility for protecting customers cannot rest entirely on individuals. Customers should safeguard their PINs, passwords and one-time passwords, avoid suspicious links and verify requests for personal information through official banking channels. But financial institutions also have a duty to ensure that employees do not request or retain sensitive customer credentials in ways that expose accounts to misuse. Banks must provide secure procedures for helping customers who experience technical problems, particularly elderly people and others who may be less familiar with digital banking.
The question of who bears the financial loss after a fraudulent transaction can also become a source of conflict between customers and banks. A former senior bank manager told Saturday PUNCH that responsibility may depend on how the fraud occurred, the evidence available and whether the institution or the customer failed to follow appropriate security procedures. Banks generally investigate disputed transactions to determine how credentials were obtained, whether security warnings were ignored and whether internal controls were properly applied. The difficulty for customers is that they may have little access to the technical evidence needed to understand how a transaction was authorised.
For elderly customers such as Uwaila, the consequences can be particularly severe. Savings accumulated over decades may represent money intended for retirement, medical expenses, housing and everyday living costs. Losing those funds can create financial insecurity at a stage of life when recovering from the loss may be difficult. The reported collapse of the 73-year-old woman after discovering the disappearance of her savings also illustrates the personal distress that can accompany financial fraud, beyond the figures recorded in industry reports.
For the banking industry, repeated security failures can damage public confidence in digital financial services. Nigeria has invested heavily in expanding electronic payments, mobile banking and financial inclusion, allowing millions of people to access services without visiting physical branches. But that progress depends on customers believing that their money and personal information are safe. If customers begin to associate routine banking assistance with the possibility of losing their savings, confidence in digital services could weaken, affecting legitimate transactions and the wider financial inclusion agenda.
Data product manager and AI strategist Oladipo Gbolahan told Saturday PUNCH that the damage caused by cyber breaches extends beyond the money stolen. Financial institutions may have to divert staff and resources from development and customer service to investigations, system recovery and regulatory compliance. Additional security measures can also make transactions more complicated for legitimate customers, while uncertainty about how an institution responds to an incident can undermine confidence in the entire payments ecosystem.
Gbolahan argued that banks should design their systems on the assumption that passwords or other credentials may eventually be compromised. That means limiting the damage a stolen credential can cause through transaction limits, restricted privileges, real-time detection systems and clear ownership of sensitive data. He also stressed that customers should receive timely information when incidents occur and be given meaningful control over the security limits applied to their accounts.
The latest cases and figures point to a problem that cannot be addressed through customer awareness campaigns alone. Banks must strengthen internal oversight, independently test their systems, monitor privileged employee accounts and ensure that suspicious transactions trigger immediate investigation. Regulators and law enforcement agencies must also maintain effective reporting and prosecution processes so that employees or external criminals found responsible for financial theft cannot simply move between institutions and repeat the same operations.
For customers, the immediate lesson is to treat requests for PINs, passwords and one-time passwords with extreme caution, including requests made by people claiming to be bank employees. A customer experiencing a problem with a mobile application should use verified bank channels and should never disclose a secret PIN or password to someone claiming to need it to repair the service. Anyone who notices an unauthorised transaction should contact the bank immediately, request that affected cards and digital access be secured, preserve transaction alerts and other evidence, and report the incident to the appropriate authorities.
The reported theft involving Uwaila remains unresolved in the available account, and there is no established finding that the bank or the employee she described was responsible. But her experience, alongside documented investigations involving substantial sums and alleged insider participation, underscores the scale of the challenge facing Nigeria's financial sector. With billions of naira lost to fraud over recent years, the central issue is no longer simply whether banks can offer faster digital services, but whether they can protect the people whose savings and livelihoods depend on them.